Let us know how we can help
Sales & Pricing
Speak to a rep about your business needs

Help & Support
See our product support options
General inquiries and locations
Contact us

 Control-M + Azure Resource Manager
Your Azure Resource Manager workflow starts before a deployment ever executes — and it can fail when something upstream breaks. An ARM template in Azure Blob Storage isn’t ready. A Terraform infrastructure job runs long. Control-M orchestrates the full chain: template arrival, infrastructure preparation, Azure deployment, and downstream validation.
common workflow issues
Does this sound like your week?
These aren’t edge cases. They’re the normal operating conditions for teams running Azure Resource Manager deployments across multiple tools. Here’s how Control-M handles each one.
TEMPLATE READINESS
Your ARM template changed. The production deployment started before validation finished.
Control-M makes the Azure Resource Manager deployment dependent on upstream validation completing successfully. The deployment is released only after its required predecessor reaches the expected state, preventing an infrastructure change from starting before the workflow is ready.
CROSS-TOOL DEPENDENCY
Terraform finished late. Your Azure deployment was already scheduled for 2:00 AM.
Control-M replaces disconnected schedules with explicit cross-tool dependencies. The Azure Resource Manager job waits for the required Terraform workflow to complete successfully, then proceeds automatically — eliminating timing assumptions between infrastructure stages.
DEPLOYMENT FAILURE
Azure returned a failed deployment. Downstream configuration is still queued.
Control-M monitors Azure Resource Manager job status, results, and output and applies workflow dependencies before releasing subsequent jobs. A failed deployment can stop the dependent path, containing the failure before configuration or application workloads continue.
SLA RISK
The environment must be ready by 6:00 AM. Provisioning is running late.
Control-M connects Azure Resource Manager execution to the SLA of the wider production workflow. Teams can track infrastructure provisioning alongside upstream and downstream jobs, identify delivery risk, and intervene before a delayed deployment affects the business service.
CREDENTIAL MANAGEMENT
A client secret changed. Your overnight infrastructure deployment can no longer authenticate.
Control-M centralizes Azure Resource Manager credentials in a connection profile and supports Service Principal or Managed Identity authentication. Service Principal secrets can also be retrieved through supported external vault integrations, reducing credential handling inside individual jobs.
Control‑M + Azure Resource Manager
Control‑M + Azure Resource Manager
|
API and automation capabilities |
Automation API · JSON job definitions · Create Deployment · Update Deployment · resource-group targeting · JSON deployment properties · Control-M CLI provisioning |
|
Deployment models & infrastructure flexibility |
Control-M SaaS · Linux Agent · Windows Agent · hybrid environments · on-premises Agent with Service Principal · Azure VM Agent with Managed Identity · custom Azure Resource Manager endpoint |
|
Security posture |
secure connection profiles · Service Principal · Managed Identity · Azure tenant ID · Client Secret · external vault support for Service Principal secrets · managed identity client ID |
|
Incident response & MTTR enablement |
deployment status monitoring · results and output capture · configurable status polling · downstream cascade prevention · dependency-based failure containment · SLA job attachment · centralized workflow monitoring |
end-to-end orchestration
One production workflow. Every tool in the stack.
Control-M orchestrates workflows across Azure Resource Manager, Terraform, Azure Blob Storage, Azure Functions, Azure Data Factory, APIs, and file transfers in a single job flow — with dependency tracking, SLA visibility, and automated recovery across all of them.
- Cross-tool dependency: Terraform → Azure Resource Manager deployment → Azure Function → application validation
- Data-aware triggers: file arrival, API event, infrastructure job completion, deployment status
|
Azure Resource Manager |
Create Deployment · Update Deployment · status monitoring · results and output |
|
Terraform |
workspace execution · infrastructure provisioning · cross-tool dependency control |
|
Azure Blob Storage |
template delivery · file-arrival dependency · workflow handoff |
|
Azure Functions |
function execution · downstream automation · completion tracking |
|
Azure Data Factory |
pipeline orchestration · status tracking · downstream dependencies |
|
REST APIs |
service invocation · workflow handoff · application validation |
|
File transfers |
secure delivery · arrival detection · downstream triggering |
MONITOR WORKLOADS
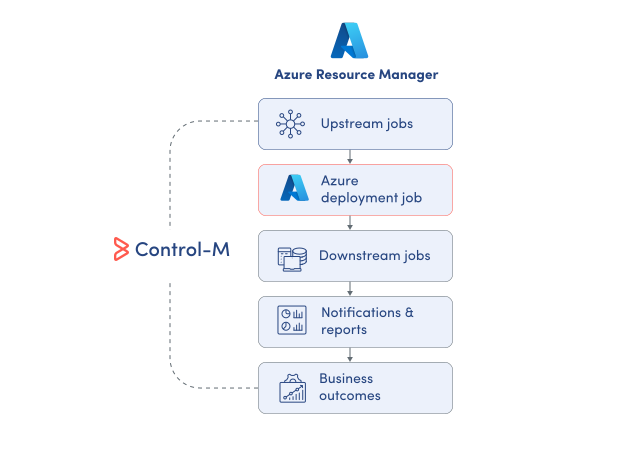
Monitor Azure deployments across the full workflow.
Azure Resource Manager reports what happens inside the Azure deployment, but production execution often spans tools outside that boundary. Control-M provides centralized visibility into the Azure job and the dependencies surrounding it:
-
Deployment execution status
-
Job results and output
-
Upstream and downstream dependencies
-
Cross-tool workflow status
-
Runtime and failure visibility
SLA ASSURANCE
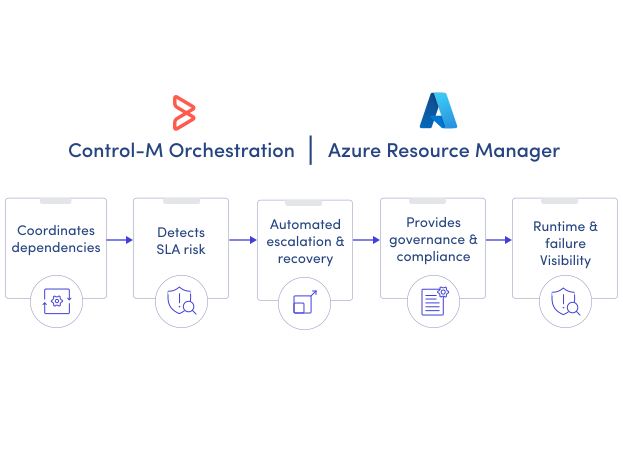
Keep infrastructure provisioning aligned with production SLAs.
A successful Azure deployment can still be too late for the service that depends on it. Control-M connects infrastructure execution to the end-to-end workflow, providing SLA visibility beyond the individual deployment:
-
End-to-end SLA tracking
-
Deployment dependency visibility
-
SLA risk identification
-
Downstream execution control
-
Centralized operational monitoring
Documentation
Bring order to complex workflows
Learn how Control-M helps teams orchestrate complex processes with greater visibility, coordination, and control.
